Compliance work, done as you go.
Screening, verification and diligence run inside the workflows your team already uses, and every action lands in the activity log.
Screened from the first contact
Four checks that run without anyone remembering to run them.
-
Sanctions screening
Every contact checked against OFAC and other sanctions lists, with PEP screening, at onboarding and continuously after.
-
KYC and KYB
Identity and business verification through a portal link, at Light, Standard or Enhanced depth.
Diligence levels -
Wallet screening and verification
Wallets are screened, and confirmed with a test payment before the first real one.
How verification works -
Activity log
Every approval, change and payment, with who did it and when.
See the activity log
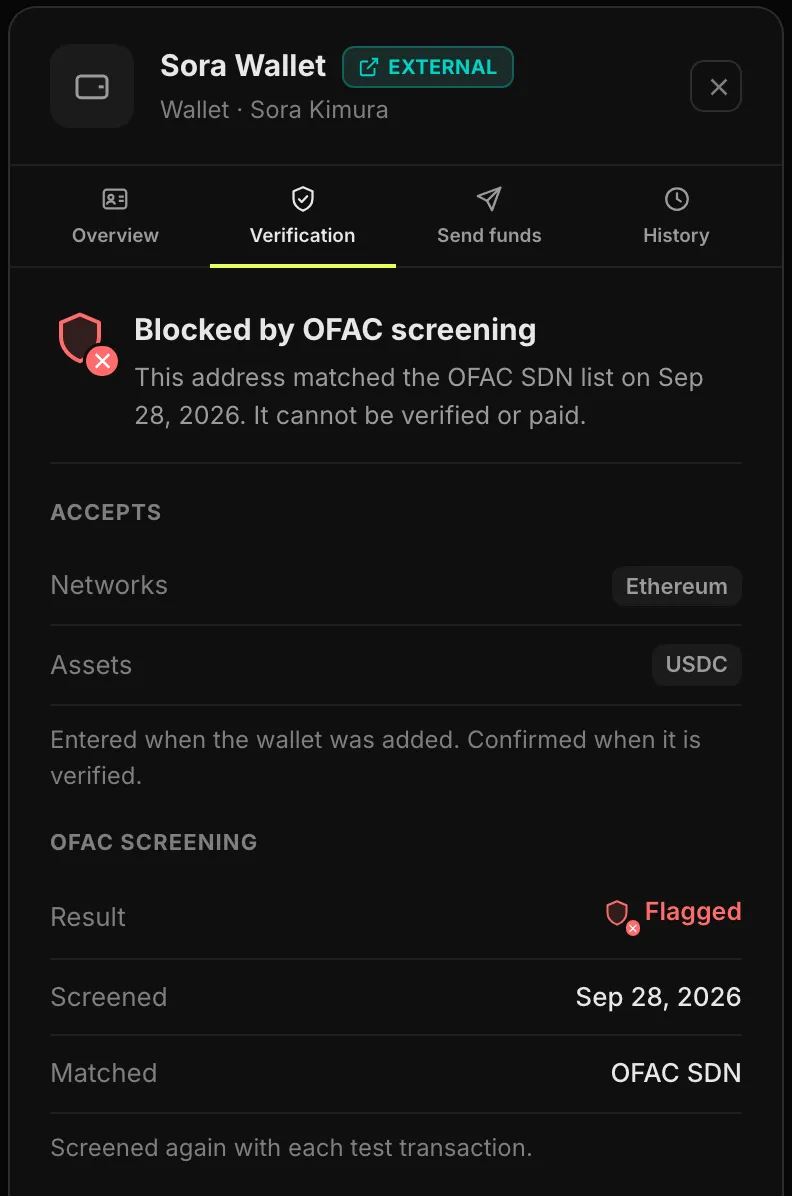
A flagged wallet cannot be paid
When a counterparty's wallet matches the OFAC sanctions list, it is blocked on the spot. It cannot be verified, and nobody can send it a payment, however many approvals they collect.
The match stays on the record: which list, and when. The wallet is screened again with every test transaction, so a clean result does not go stale.
Ready when someone asks
The evidence is kept as the work happens, so answering a request is finding it, not rebuilding it.
| Who asks | Where the answer already is |
|---|---|
| Your bank, refreshing its KYB | Your entities' formation documents and records, filed in Company Files |
| An auditor, testing payments | Each payment's process record: who raised it, who approved it, how it was executed |
| Anyone checking a counterparty | That contact's verification history: which checks, when, and when each was refreshed |
| Your board, asking who can move money | Your approval rules, and the activity log behind every change to them |